
Introduction
Software quality is one of the most important factors in the success of any software product. Whether a business is developing a web application, mobile app, enterprise platform, or cloud-based solution, users expect software to be reliable, secure, fast, and easy to use. However, achieving these expectations requires more than effective coding and testing. It starts with proper planning throughout the Software Development Life Cycle (SDLC).
SDLC planning provides a structured approach to developing software, from gathering requirements and designing the system to development, testing, deployment, and maintenance. When every phase is planned carefully, development teams can identify potential risks early, reduce defects, improve collaboration, and deliver software that meets business and user expectations.
Poor SDLC planning, on the other hand, can lead to unclear requirements, missed deadlines, unexpected costs, insufficient test coverage, and critical production defects. These problems often occur when quality assurance is treated as a final step rather than an essential part of the entire development process.
In this blog, we will explore how better SDLC planning can improve software quality, the best practices development and QA teams should follow, and the practical steps organizations can take to build a more reliable software development process.
What Is SDLC Planning?
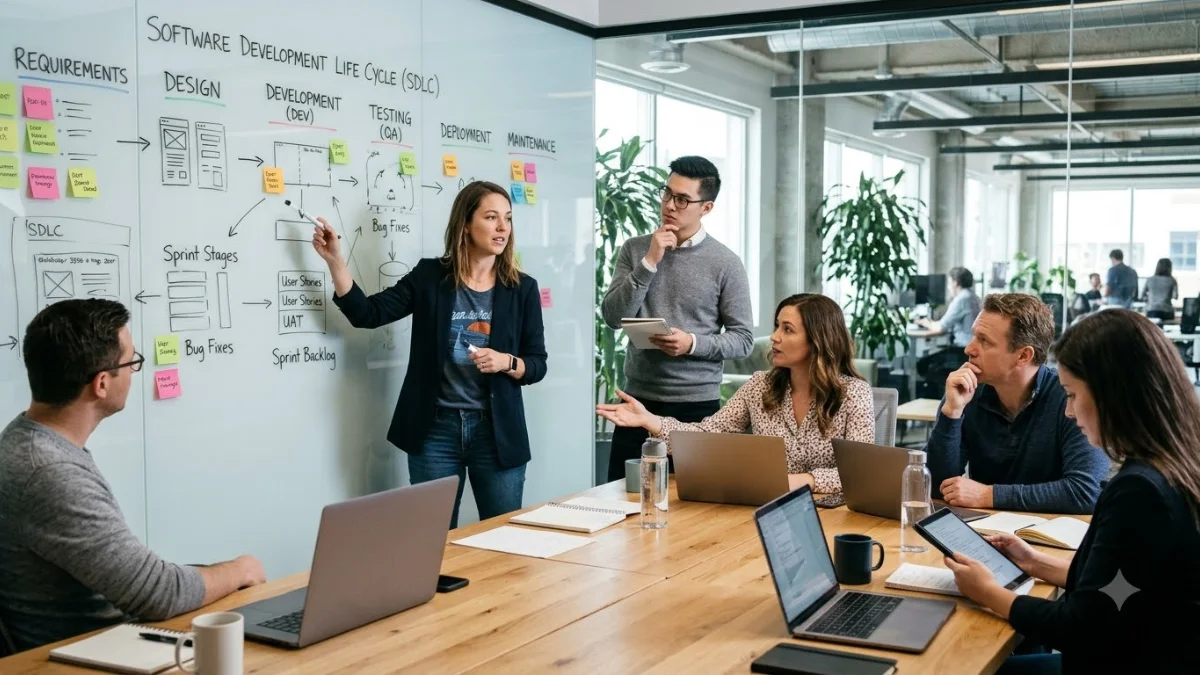
The Software Development Life Cycle (SDLC) is a structured process used to plan, design, develop, test, deploy, and maintain software applications. SDLC planning defines how a software project will be executed, including its scope, requirements, resources, timeline, risks, quality standards, and deliverables.
Effective planning ensures that everyone involved in a project understands what needs to be developed, how the work will be completed, and how success will be measured.
A typical SDLC consists of the following phases:
- Requirement Analysis: Understanding business needs, user expectations, and technical requirements.
- Planning: Defining project scope, timelines, budgets, resources, and potential risks.
- System Design: Creating the architecture, workflows, database structures, and user interface designs.
- Development: Writing code according to approved requirements and design specifications.
- Testing: Verifying functionality, performance, security, usability, and compatibility.
- Deployment: Releasing the application into the production environment.
- Maintenance: Monitoring performance, resolving defects, and implementing improvements.
Each phase contributes to the overall quality of the final product. When teams plan these activities effectively, they can prevent many issues before they affect users.
Why Is SDLC Planning Important for Software Quality?
Software defects are not always caused by coding mistakes. Many problems originate much earlier in the development process, particularly when requirements are incomplete, designs are unclear, or testing activities are poorly planned.
SDLC planning helps organizations establish a quality-focused approach before development begins.
1. Reduces Development Errors
Clear requirements and well-defined acceptance criteria help developers understand exactly what they need to build. When expectations are documented properly, teams are less likely to make incorrect assumptions or implement unnecessary functionality.
For example, suppose a company is developing an online payment application. If the requirements do not clearly explain how failed transactions, duplicate payments, and refunds should be handled, developers may implement inconsistent behavior.
By discussing these scenarios during the planning phase, the team can define the expected behavior before coding starts. QA engineers can then use the same requirements to prepare test scenarios and validate the implementation.
This approach reduces misunderstandings, rework, and avoidable defects.
2. Improves Test Coverage
Testing is more effective when it is planned alongside development rather than introduced after the application has been completed.
During SDLC planning, teams can identify the features, workflows, integrations, and business risks that require testing. This helps QA engineers prepare test strategies that cover both expected functionality and potential failure scenarios.
A well-planned testing process should consider:
- Positive and negative test scenarios.
- Boundary value and input validation testing.
- Integration and end-to-end workflows.
- Regression testing for existing functionality.
- Performance and load testing.
- Security and access-control testing.
- Cross-browser and device compatibility.
- Accessibility and usability requirements, where applicable.
For example, an e-commerce application should not only test whether users can place orders successfully. It should also verify inventory updates, payment failures, discount calculations, order cancellations, and refund processing.
Identifying these scenarios early helps prevent important test cases from being overlooked.
3. Minimizes Project Risks
Every software project involves risks related to technology, requirements, deadlines, resources, integrations, and security. Without proper planning, these risks may remain hidden until they cause delays or failures.
SDLC planning encourages teams to identify and assess risks before development progresses too far.
For example, if a project depends on a third-party payment gateway, the team should evaluate API documentation, authentication requirements, rate limits, error responses, and sandbox availability early in the project.
Similarly, if an application must support thousands of concurrent users, performance requirements should be established before the architecture is finalized.
Early risk identification gives teams more time to develop mitigation strategies and reduces the likelihood of expensive last-minute changes.
Best Practices for Improving Software Quality Through SDLC Planning
Organizations can improve software quality by introducing consistent planning practices throughout the development life cycle.
1. Define Clear and Measurable Requirements
Requirement analysis is the foundation of successful software development. If requirements are incomplete or ambiguous, even technically correct software may fail to meet user expectations.
Before development begins, teams should collaborate with business stakeholders, product owners, designers, developers, and QA engineers to understand the intended functionality.
Requirements should explain what the system must do, who will use it, and what conditions determine successful behavior.
Best practices include:
- Documenting functional and non-functional requirements.
- Defining clear acceptance criteria for each feature.
- Identifying business rules and workflow dependencies.
- Recording assumptions, constraints, and external integrations.
- Reviewing requirements with relevant stakeholders.
- Maintaining traceability between requirements, test cases, and defects.
For example, instead of writing “The login page should be secure,” a requirement could specify that users must authenticate using approved credentials, repeated failed attempts must trigger defined protective controls, and access to restricted pages must require an authenticated session.
Clear requirements reduce ambiguity and help QA teams create meaningful tests.
2. Involve QA Engineers Early in the SDLC
One of the most effective ways to improve software quality is to involve QA engineers from the beginning of the project.
When testers participate only after development is complete, they may discover requirement gaps, design weaknesses, and integration problems that are expensive to fix.
Early QA involvement allows testers to review requirements, identify missing scenarios, assess risks, and provide feedback before implementation begins.
QA engineers can contribute by:
- Reviewing requirements for ambiguity and testability.
- Identifying missing acceptance criteria.
- Preparing test scenarios during requirement analysis.
- Reviewing designs for usability and potential failure points.
- Advising on test data and environment requirements.
- Identifying opportunities for automation.
- Highlighting risks that require additional testing.
This approach is closely related to shift-left testing, which moves quality activities earlier in the development process.
By identifying issues before code is written, teams can reduce rework and improve delivery efficiency.
3. Choose the Right SDLC Model
The SDLC model influences how teams plan development, manage changes, conduct testing, and deliver software.
Different projects require different approaches, so selecting the right model is an important planning decision.
Waterfall Model: This approach follows a sequential process in which phases are generally completed before the next phase begins. It can be useful when requirements are stable, clearly defined, and subject to formal approval.
Agile Model: Agile divides development into smaller iterations, allowing teams to gather feedback, test frequently, and adapt to changing requirements. It is often suitable for products that evolve continuously.
V-Model: The V-Model emphasizes corresponding testing activities for development stages. It encourages teams to plan verification and validation early.
DevOps-Oriented Approach: DevOps emphasizes collaboration between development and operations, supported by automation, continuous integration, continuous delivery, monitoring, and feedback.
When selecting an SDLC model, organizations should consider project complexity, requirement stability, regulatory obligations, team experience, release frequency, and customer involvement.
The best approach is the one that supports the project’s needs while maintaining appropriate quality controls.
4. Establish a Strong Test Strategy During Planning
A test strategy defines the overall approach to validating software quality. It helps teams determine what will be tested, how testing will be performed, which resources are required, and what risks must be addressed.
Without a clear strategy, testing may become inconsistent or focus too heavily on easy-to-test features instead of critical business workflows.
A strong test strategy should define:
- Testing scope and objectives.
- Test levels, including unit, integration, system, and acceptance testing.
- Manual and automated testing responsibilities.
- Test environments and test data requirements.
- Risk-based testing priorities.
- Defect severity and priority definitions.
- Entry and exit criteria.
- Reporting methods and quality metrics.
For example, a banking application may require extensive validation of transaction accuracy, access controls, audit trails, and failure recovery. A content website may prioritize publishing workflows, browser compatibility, accessibility, and page performance.
The strategy should reflect the actual risks and quality requirements of the product.
5. Set Realistic Timelines and Allocate Resources Properly
Unrealistic deadlines are a common cause of software quality problems. When teams are pressured to release software without sufficient time for testing, they may skip important validation activities or postpone defect fixes.
Effective SDLC planning includes realistic estimates for requirements analysis, design, implementation, testing, defect resolution, and release preparation.
Project managers should account for dependencies, technical uncertainty, integration complexity, and the possibility of rework.
Resource planning should also consider the availability of developers, manual testers, automation engineers, performance testers, security specialists, and infrastructure support.
Best practices include:
- Breaking large deliverables into manageable tasks.
- Estimating work with input from the people performing it.
- Including time for testing and defect retesting.
- Planning for regression testing after significant changes.
- Identifying resource constraints early.
- Reviewing progress regularly and adjusting priorities.
A realistic schedule does not guarantee a defect-free product, but it provides teams with a better opportunity to validate critical functionality before release.
6. Use Risk-Based Testing to Prioritize Critical Features
Not every software feature carries the same level of risk. A failure in a payment transaction, authentication process, or data synchronization workflow may have much greater consequences than a minor visual issue.
Risk-based testing helps teams prioritize testing according to the likelihood of failure and its potential impact.
During SDLC planning, teams should identify critical features, complex integrations, frequently changed components, sensitive data flows, and areas with a history of defects.
A practical risk assessment can consider:
- Business impact if the feature fails.
- Probability of failure.
- Technical complexity.
- Security and privacy implications.
- Frequency of use.
- Dependencies on external systems.
- Previous defect patterns.
For example, in an e-commerce application, payment processing, order creation, inventory management, and customer authentication may receive higher testing priority than less critical informational pages.
Risk-based testing does not mean ignoring lower-risk features. It means allocating testing effort according to business priorities and available resources.
7. Integrate Test Automation Into the Development Workflow
Test automation can improve consistency, accelerate feedback, and reduce repetitive manual work when implemented strategically.
However, automation should be planned around stable, valuable test scenarios rather than introduced without a clear purpose.
During SDLC planning, teams should identify which tests provide the greatest benefit from automation.
Common candidates include:
- Unit tests for business logic.
- API tests for service integrations.
- Regression tests for frequently used workflows.
- Smoke tests for deployment verification.
- Data validation checks.
- Repeated cross-browser tests for critical user journeys.
Tools such as Selenium, Playwright, and Cypress can support automated web application testing. API testing tools and CI/CD platforms can further integrate validation into the delivery pipeline.
For example, after a developer submits code, a CI pipeline can run unit tests, API tests, and selected browser tests. If a critical check fails, the team receives feedback before the change moves further through the delivery process.
Organizations should also plan for automation maintenance, test reliability, execution time, reporting, and ownership. A large automation suite is not necessarily effective if its tests are unstable or provide little business value.
8. Maintain Continuous Communication Between Teams
Software quality is a shared responsibility. Developers, QA engineers, product owners, designers, security specialists, and operations teams all influence the final result.
Poor communication can lead to inconsistent assumptions, delayed defect resolution, duplicated work, and misunderstandings about release readiness.
SDLC planning should establish clear communication practices and responsibilities.
Effective practices include:
- Conducting requirement and design review meetings.
- Sharing acceptance criteria before development starts.
- Discussing blockers during regular team check-ins.
- Using a shared issue-tracking system.
- Documenting technical decisions.
- Reviewing defects collaboratively.
- Agreeing on release approval responsibilities.
In Agile teams, sprint planning, daily stand-ups, backlog refinement, and retrospectives can help maintain alignment.
When teams share information consistently, they can identify problems sooner and make better decisions about software quality.
9. Plan for Security and Performance From the Beginning
Security and performance should not be treated as optional activities that happen only before release.
If these requirements are considered too late, the application architecture may already contain weaknesses that are difficult to correct.
During SDLC planning, teams should define appropriate security and performance expectations based on the product’s purpose, users, data, and expected workload.
Security planning may include:
- Authentication and authorization requirements.
- Secure handling of sensitive information.
- Input validation and protection against common vulnerabilities.
- Dependency and configuration checks.
- Security testing and remediation procedures.
- Access-control and audit requirements.
Performance planning may include:
- Expected concurrent users and transaction volumes.
- Response-time objectives.
- Load and stress testing.
- Resource utilization monitoring.
- Scalability and recovery expectations.
- Performance regression checks.
For example, a healthcare platform handling confidential information may require strict access controls and secure data handling, while a ticket-booking platform may need to withstand sudden traffic spikes during high-demand events.
Planning these requirements early helps teams design systems that are not only functional but also secure, responsive, and resilient.
10. Establish Clear Entry and Exit Criteria
Entry and exit criteria help teams determine when a phase of development or testing is ready to begin and when it can be considered complete.
Without these criteria, work may progress despite missing requirements, incomplete environments, or unresolved critical defects.
Examples of entry criteria for system testing include:
- Required functionality has been deployed to the test environment.
- The test environment is available and configured.
- Necessary test data has been prepared.
- Critical dependencies are accessible.
- Initial smoke tests have passed.
Examples of exit criteria include:
- Planned critical test scenarios have been executed.
- All release-blocking defects have been resolved or formally accepted.
- Required regression tests have passed.
- Agreed coverage and quality targets have been evaluated.
- Remaining risks have been documented.
- Relevant stakeholders have reviewed the results.
Exit criteria should reflect project risk rather than rely on a single universal pass percentage. For example, a product may require zero open critical defects, while lower-severity issues can be accepted only with documented approval and an agreed resolution plan.
These criteria make release decisions more transparent and consistent.
11. Use Quality Metrics to Measure Progress
Metrics help teams understand whether their SDLC planning practices are improving software quality.
However, metrics should support better decisions rather than encourage teams to optimize numbers without improving the product.
Useful quality indicators include:
Defect Density: Measures the number of defects relative to a defined amount of software, such as code size or functionality delivered.
Defect Leakage: Tracks defects discovered after a release compared with defects identified during earlier testing stages. The calculation should use a consistent definition.
Test Coverage: Indicates how much of the defined requirements, code, or functionality is covered by testing. Coverage should be interpreted alongside test effectiveness.
Test Pass Rate: Measures the proportion of executed tests that pass during a particular test cycle.
Defect Resolution Time: Tracks how long it takes to resolve reported defects.
Change Failure Rate: Measures how frequently deployed changes result in failures that require intervention, rollback, or remediation, using a clearly defined calculation.
Escaped Defects: Tracks defects discovered by users or in production after release.
Teams should establish baselines, monitor trends over time, and investigate the reasons behind changes. No single metric can fully represent software quality.
For instance, a high test pass rate may look positive, but it does not prove quality if important scenarios were never tested.
12. Conduct Regular Reviews and Improve the Process
SDLC planning should be an evolving activity rather than a document created once at the beginning of a project.
As development progresses, teams gain new information about technical limitations, user behavior, defects, dependencies, and delivery risks.
Regular reviews help teams adapt their plans to these changes.
Useful activities include:
- Reviewing project progress and upcoming dependencies.
- Assessing new or changing requirements.
- Analyzing recurring defects.
- Reviewing test coverage and automation effectiveness.
- Evaluating production incidents.
- Conducting sprint retrospectives or project post-mortems.
- Updating standards and checklists based on lessons learned.
For example, if several production defects originate from incomplete API validation, the team can improve requirement templates, add API contract checks, and expand negative testing in future releases.
Continuous improvement enables organizations to strengthen their SDLC practices over time.
How SDLC Planning and STLC Work Together
The Software Development Life Cycle and Software Testing Life Cycle are closely connected, but they serve different purposes.
SDLC provides the broader framework for planning and delivering software, while STLC organizes the activities required to validate its quality.
When these processes are aligned, testing becomes a planned part of development rather than a separate activity performed at the end.
For example:
| SDLC Phase | Related QA/STLC Activities |
|---|---|
| Requirement analysis | Requirement reviews, testability analysis, initial test scenarios |
| Planning | Test strategy, estimates, risk assessment, resource allocation |
| System design | Design reviews, integration planning, test environment planning |
| Development | Unit testing, API checks, test case preparation, code-level validation |
| Testing | Functional, integration, regression, performance, and security testing |
| Deployment | Smoke testing, release validation, rollback readiness |
| Maintenance | Production monitoring, defect analysis, regression testing |
This alignment enables QA teams to prepare earlier, identify risks sooner, and provide continuous feedback to developers.
It also supports better traceability between requirements, implemented features, test results, and defects.
Common SDLC Planning Mistakes That Affect Software Quality
Even experienced teams can encounter problems when planning activities are incomplete or poorly coordinated.
1. Starting Development Without Clear Requirements
Ambiguous requirements cause confusion and increase the likelihood of rework. Teams should validate requirements with stakeholders and define measurable acceptance criteria before implementation begins.
2. Treating Testing as the Final Phase
Late testing leaves less time to resolve defects and can expose major design or requirement problems close to release. QA should participate throughout the development process.
3. Underestimating Testing Effort
Testing involves more than executing test cases. Teams also need time for test design, environment setup, test data preparation, defect investigation, retesting, regression testing, and reporting.
4. Ignoring Non-Functional Requirements
An application may work correctly under normal conditions but still fail under heavy load, expose sensitive data, or behave inconsistently across browsers. Performance, security, accessibility, and compatibility should be considered during planning.
5. Relying Only on Automated Tests
Automation is valuable, but it cannot replace every form of testing. Exploratory testing, usability evaluation, and human judgment remain important, particularly when requirements or user interactions are complex.
6. Making Release Decisions Without Reviewing Risks
A successful test run does not automatically mean a product is ready for release. Teams should review unresolved defects, test limitations, security concerns, operational readiness, and the potential impact of known issues.
Avoiding these mistakes helps organizations create a more predictable and quality-focused development process.
A Practical Step-by-Step Approach to Better SDLC Planning
Organizations that want to improve software quality can begin with a structured implementation plan.
Step 1: Define quality objectives. Establish what quality means for the project, including reliability, functionality, performance, security, usability, and maintainability.
Step 2: Document requirements. Work with stakeholders to define business needs, functional behavior, non-functional requirements, and acceptance criteria.
Step 3: Assess risks. Identify critical features, external dependencies, technical challenges, and potential failure points.
Step 4: Select the SDLC approach. Choose a model that fits the project’s complexity, requirement stability, delivery expectations, and regulatory environment.
Step 5: Build a testing strategy. Define test scope, test levels, automation opportunities, environments, resources, and quality gates.
Step 6: Establish team responsibilities. Clarify ownership across development, QA, product management, security, and operations.
Step 7: Integrate testing into delivery workflows. Introduce suitable automated checks, code reviews, continuous integration, and repeatable test execution.
Step 8: Monitor quality indicators. Track defects, test results, escaped issues, and delivery risks using consistent definitions.
Step 9: Review release readiness. Confirm that the agreed quality criteria are met and that remaining risks have been evaluated and accepted by the appropriate stakeholders.
Step 10: Improve continuously. Use feedback from test cycles, production incidents, and team retrospectives to refine future planning.
Following these steps helps teams establish repeatable processes without making development unnecessarily complicated.
The Role of QA Teams in Better SDLC Planning
QA teams play a central role in transforming SDLC planning into practical quality improvements.
Their responsibilities extend beyond identifying bugs. They help teams understand product risks, evaluate requirements, improve testability, and establish evidence-based release decisions.
QA engineers can contribute by reviewing requirements, designing test strategies, identifying high-risk workflows, recommending automation, validating non-functional requirements, and analyzing recurring defects.
Experienced QA professionals can also help organizations improve processes by introducing reusable test templates, risk-assessment frameworks, defect-reporting standards, test metrics, and release-readiness checklists.
For businesses managing complex applications or frequent releases, collaboration with skilled QA professionals can improve testing consistency and help identify quality issues earlier.
At QA Ninjas, the broader principle is that effective quality assurance begins with thoughtful planning, clear communication, and testing activities that align with business goals.
Conclusion
Improving software quality requires a structured approach that begins long before the first line of code is written. Better SDLC planning helps teams define clear requirements, identify risks, involve QA engineers early, allocate resources effectively, and establish meaningful quality standards.
When testing, security, performance, and operational readiness are considered throughout development, organizations can reduce avoidable defects, improve collaboration, and make more informed release decisions.
The most effective SDLC process is not necessarily the one with the most documentation or the largest number of testing activities. It is the one that helps teams identify important problems early, respond to change efficiently, and deliver software that consistently meets user and business expectations.
By treating software quality as a shared responsibility across every phase of the SDLC, organizations can build more reliable products, improve customer confidence, and create a stronger foundation for long-term growth.
Better planning leads to better testing, and better testing helps deliver better software.
For more Contact Us